Does this apply to us?
It is hard to tell whether a new or existing AI feature falls into a prohibited, high-risk, transparency or general-purpose AI (GPAI) category.
The challenge
Every company that sells an AI-powered product in the EU must now show that it meets the EU AI Act. Most product teams can't yet say whether they do.
The EU AI Act regulates AI by risk. What you must do depends on what your system does, who uses it, who it affects and where you sit in the AI value chain. For a team about to launch in Europe, compliance has become a product question as well as a legal one, and it usually comes up too late.
It is hard to tell whether a new or existing AI feature falls into a prohibited, high-risk, transparency or general-purpose AI (GPAI) category.
Hundreds of pages of legal text have to be turned into concrete product, engineering, documentation and monitoring tasks.
Obligations apply in phases and the dates keep shifting. Prohibitions and GPAI duties already apply, transparency rules have applied since August 2026, and standalone high-risk obligations move to December 2027.
AI regulation has become part of product management. Teams need a way to answer these questions before launch, not after a regulator asks.
Ancient wisdom, modern compliance
The Katha Upanishad named this choice thousands of years ago.
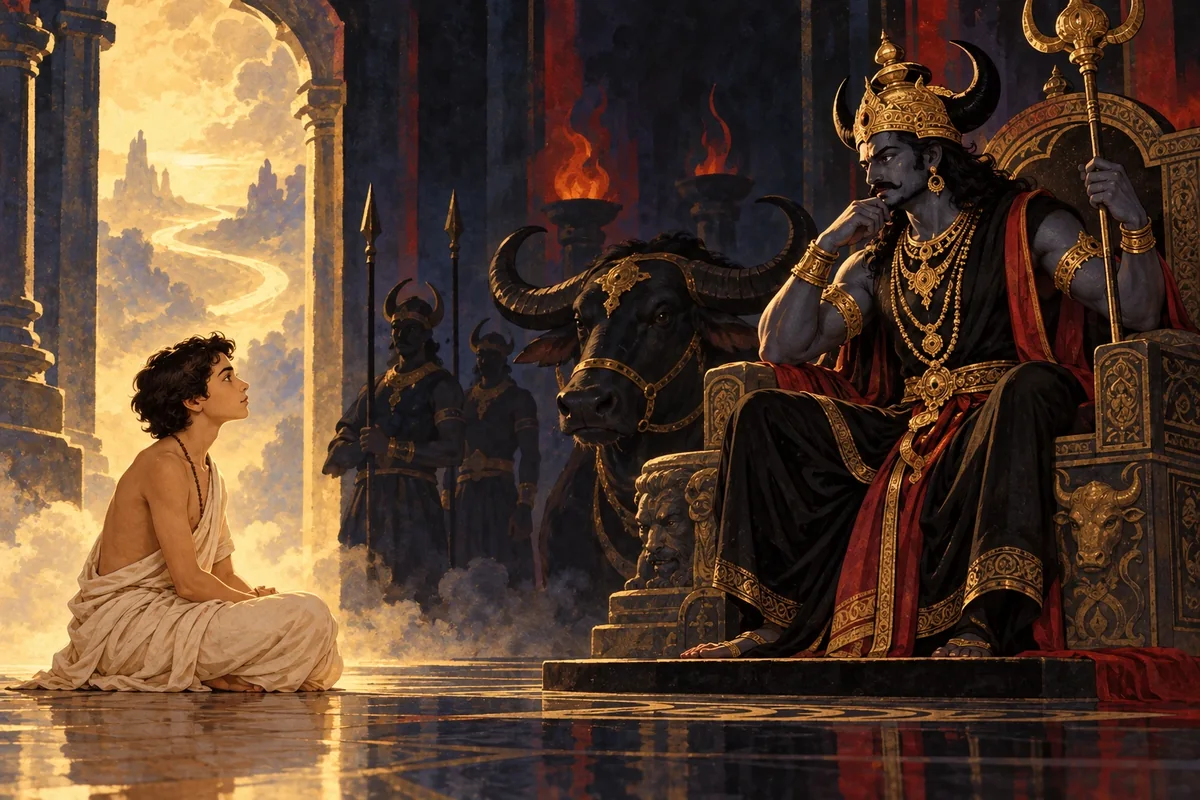
Young Nachiketa stands before Yama, the lord of death. Yama offers him wealth, kingdoms and long life. Nachiketa turns them all down and asks for true knowledge. Yama praises him because he chose Shreyas, the lasting good, over Preyas, what is pleasant right now.
Choosing what's right shouldn't mean giving up speed. With Aegis, a product manager describes the AI system in plain language, for example “We use an AI model to screen job applications and rank candidates.” The Copilot then guides them through a structured assessment:
Works out whether the system is likely to be prohibited, high-risk, subject to transparency rules, GPAI-related or minimal risk.
Turns legal requirements into practical duties for risk management, data governance, documentation, human oversight and security.
Asks targeted questions about the product, data, users and processes to find missing controls.
Produces a prioritized checklist, such as adding human oversight, documenting training data, enabling logging and disclosing AI use.
Drafts risk-assessment checklists, governance registers and questions for legal and security teams.
Tracks changing deadlines and Commission guidance so products can be reassessed over time.
Like Nachiketa, the wise team tells the two paths apart. Aegis helps you see the difference and take the right one.
What your business gains
From “Is our AI compliant?” to “Here is exactly what we need to do next.”
Find obligations at the design stage instead of the week before launch. That means fewer late-stage redesigns and fewer delayed releases.
Aegis automates the first round of research and assessment, which usually takes days of work across product, legal and engineering. Legal experts can then spend their time on the hard cases.
Catch prohibited uses and missing high-risk controls before they turn into fines of up to 7% of global turnover, forced withdrawals or reputational damage.
Risk checklists, governance registers and documentation drafts are produced as you go, so evidence exists when a regulator, auditor or notified body asks for it.
Every AI product in the portfolio gets the same repeatable assessment, whichever team built it or whichever country it launches in.
Enterprise buyers increasingly ask about AI Act compliance in their due diligence. Clear, documented answers shorten sales cycles and set you apart from competitors.
Build compliance into design instead of adding it at launch
Get requirements as concrete technical controls
Faster first-level reviews and standardized assessments
A clear view of regulatory exposure and remediation priorities
Choosing Shreyas pays off. Doing it right the first time is also the fastest way to market.
Responsible by design
Where an LLM-based Copilot can fail, how each risk is handled today, and what comes next.
What could go wrongThe model states an obligation that doesn't exist or misreads an article.
What could go wrongA high-risk system is labeled minimal risk, or the reverse.
What could go wrongDeadlines and guidance change, as the 2026 amendments did.
What could go wrongTeams treat a Copilot result as a legal sign-off.
What could go wrongProduct details shared with the Copilot leak or are used for training.
What could go wrongThe same question gets different answers on different days.
What could go wrongUsers try to push the Copilot into unsafe or misleading output.
Why it mattersAegis is itself an AI system, so it follows the rules it helps others meet.
You are interacting with an AI system. Aegis provides guidance based on the EU AI Act and is not a substitute for legal advice. Please don't share personal data you aren't authorized to share.